LAB / WAZUH / QWEN
AI-Powered SOC Lab
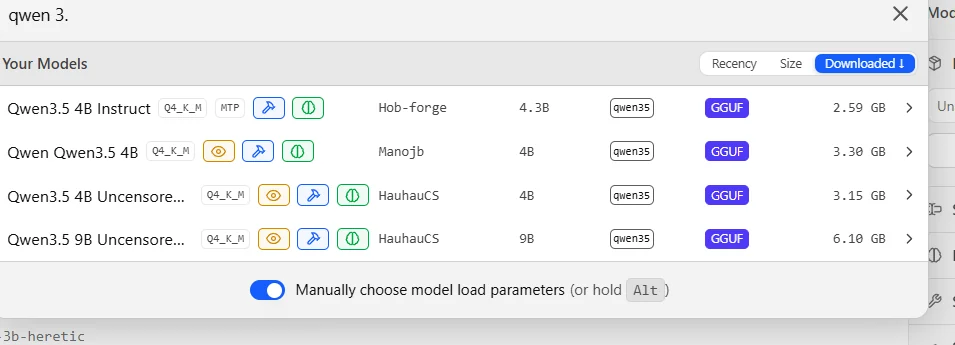
An evidence-backed defensive lab integrating Ubuntu and Wazuh SIEM with paginated OpenSearch ingestion, Python, SQLite and a local Qwen model. Manually operated, with human review required for all AI findings.
From security telemetry to evidence-based AI triage
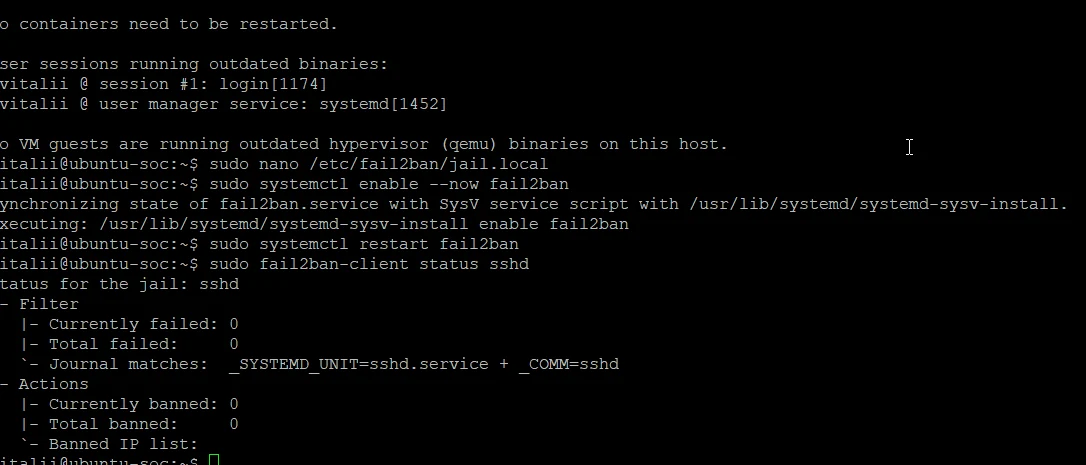
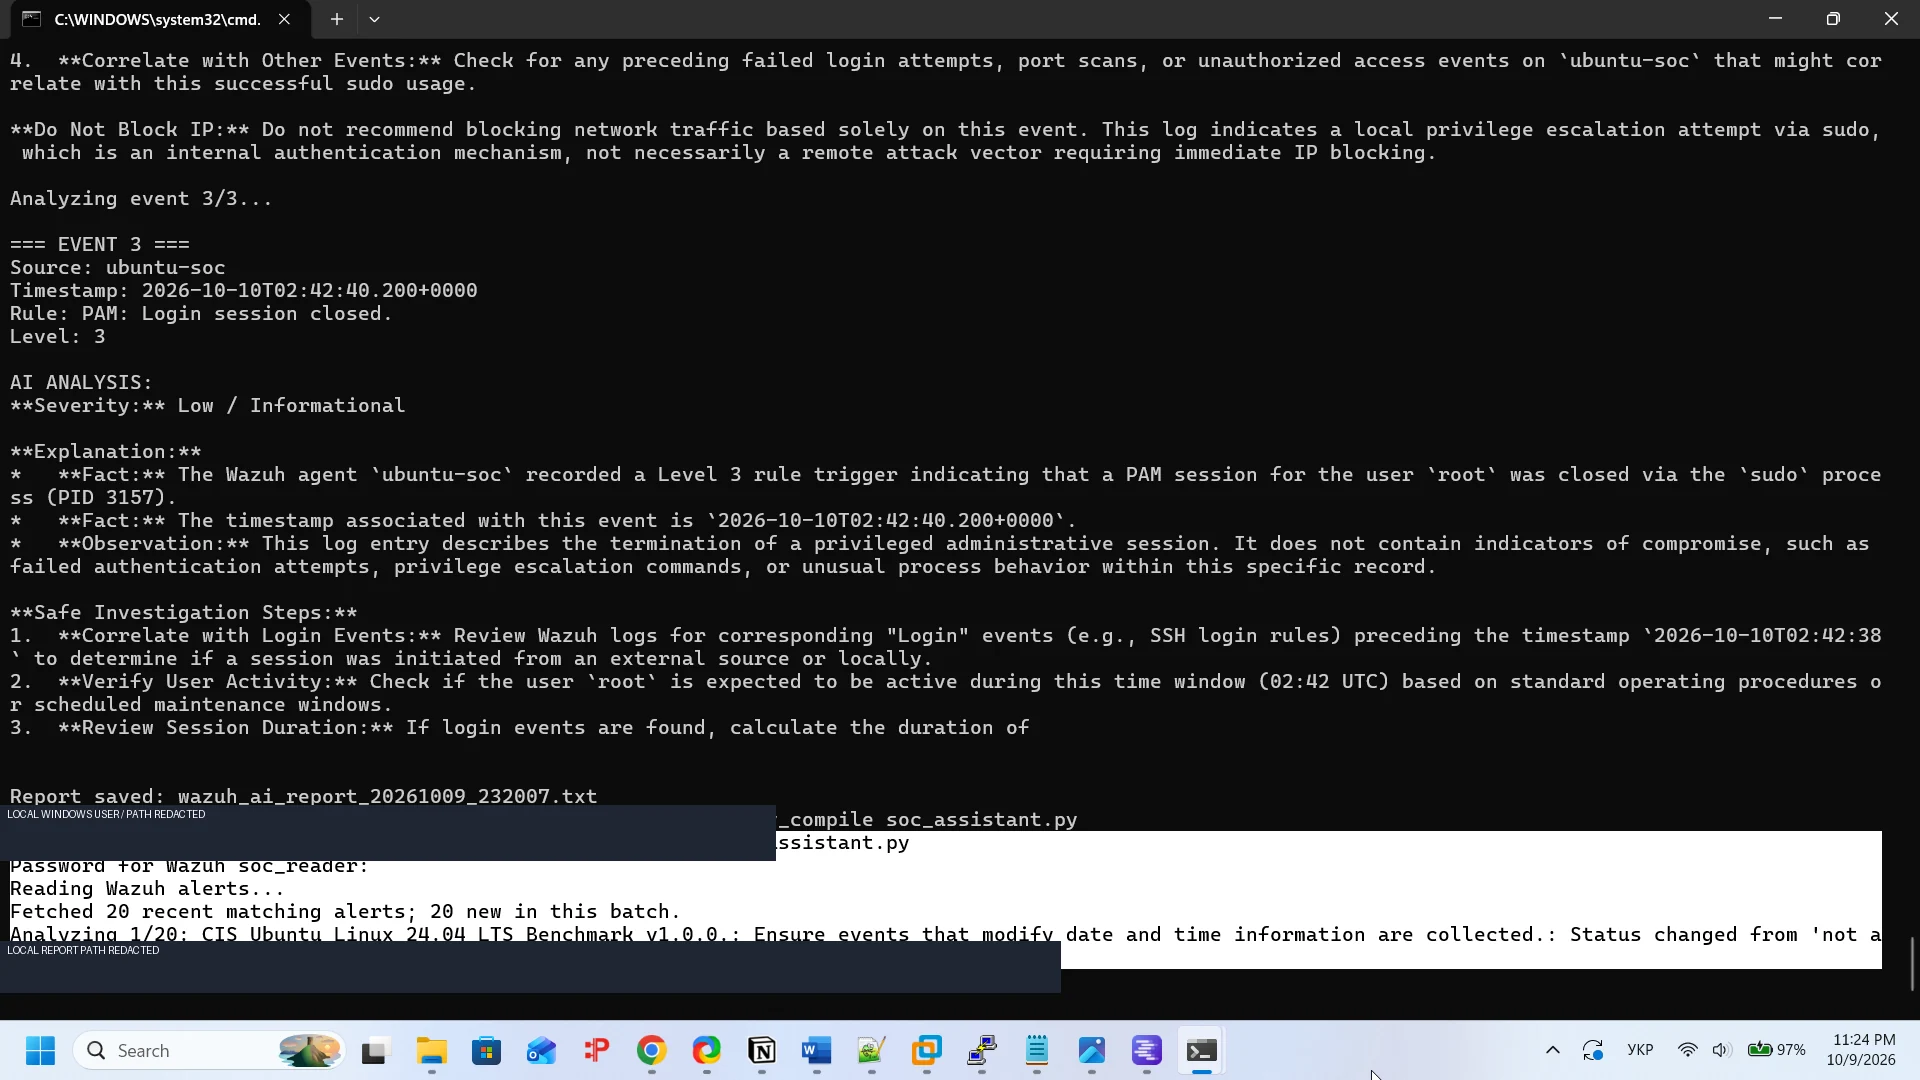
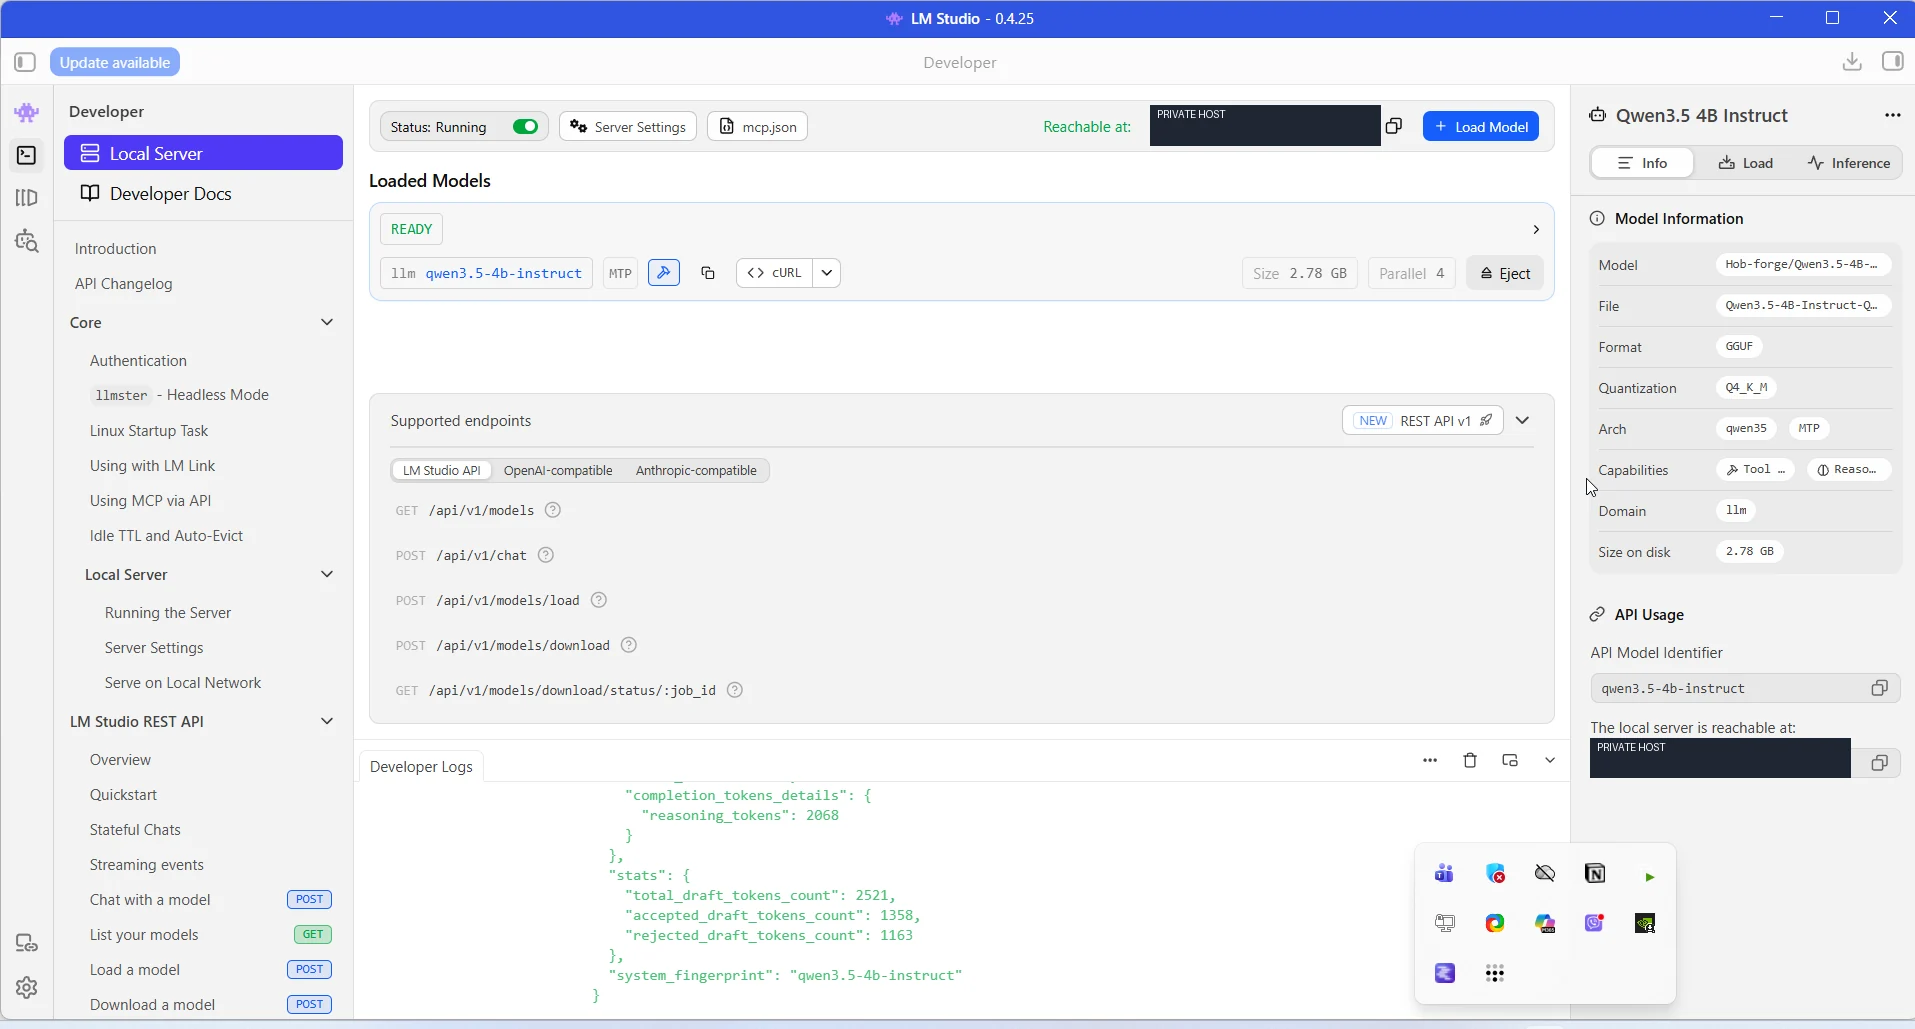
The Ubuntu endpoint sends events to Wazuh Manager and OpenSearch. Python retrieves a paginated snapshot over SSH/TLS, deduplicates alerts in SQLite, and analyzes a small manual batch through local Qwen in LM Studio. JSON validation and read-only recommendation checks constrain the report format; they do not guarantee AI accuracy.
Engineering outcome: Scroll pagination, crash-safe report recovery, basic untrusted-input guardrails, capped processing, and GitHub Actions tests. The initial CI run exposed a regex bug in the read-only filter; it was fixed and both CI jobs passed.
Limitations: This is a manually operated test lab, not a production SOC or autonomous defense system. The LLM can make incorrect assessments. The synthetic test results do not establish comprehensive prompt-injection resistance.
ORIGINAL LAB EVIDENCE
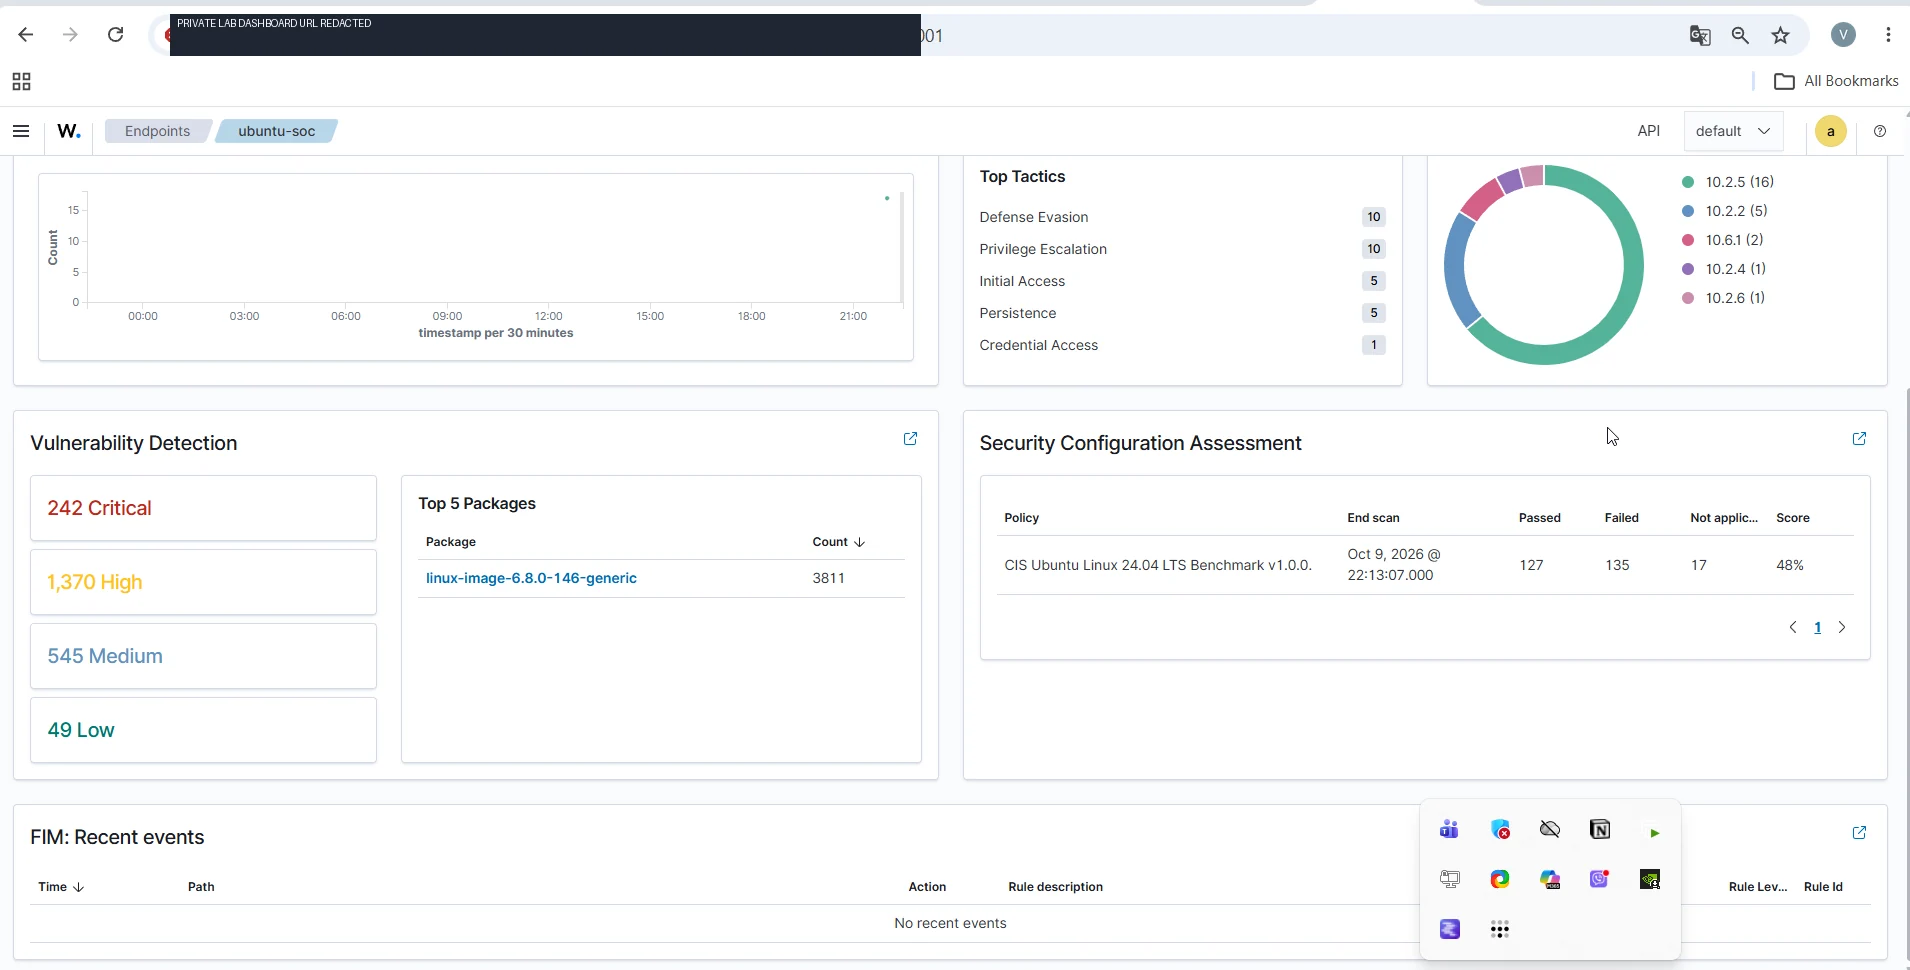
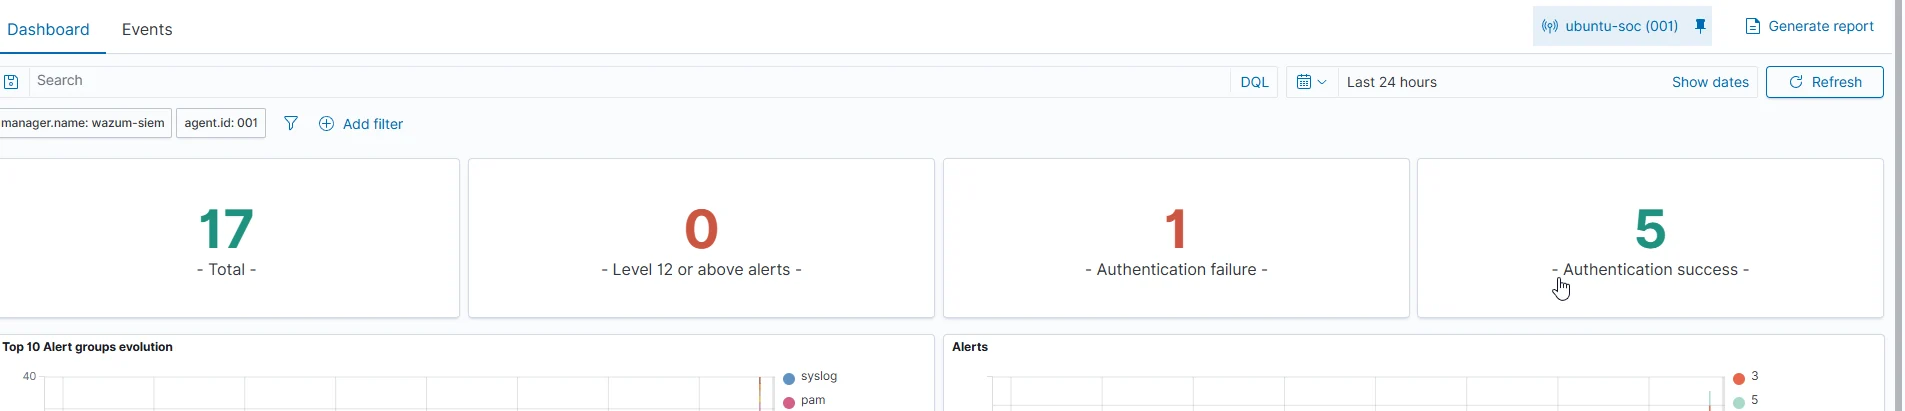
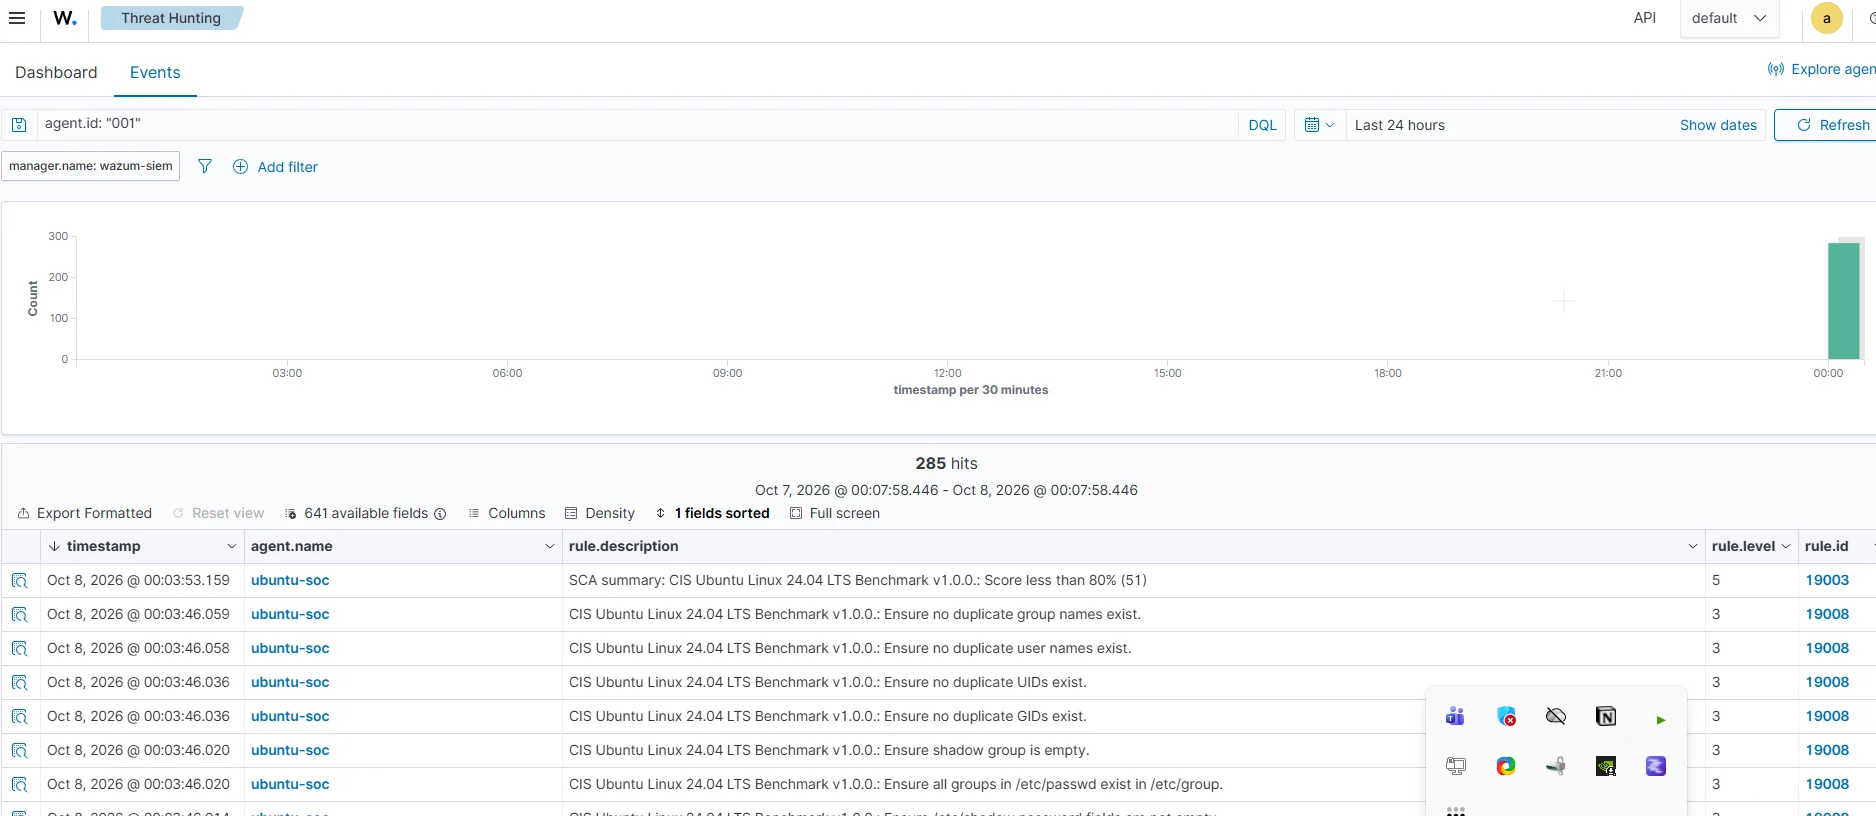
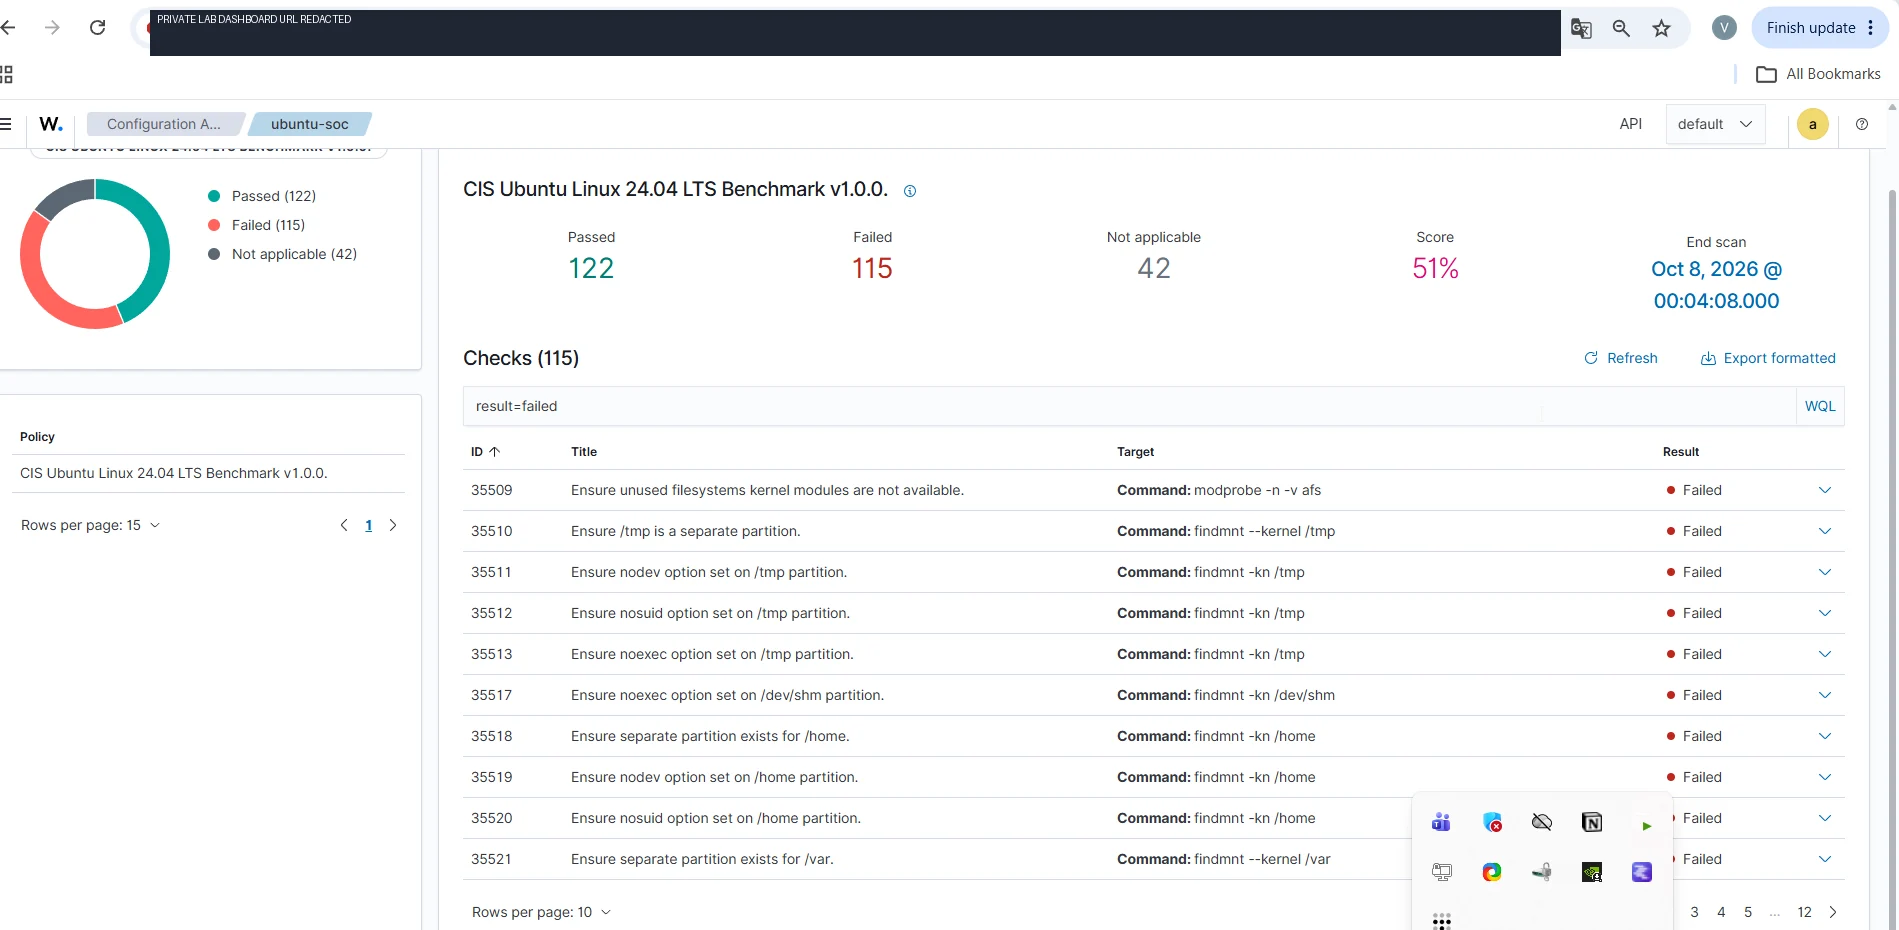
Security monitoring in practice.
The screenshots document lab interfaces and experiments, not a production security service.